Draw the Lines Before the Regulator Does: Treating Your Org Chart as a Legal Instrument
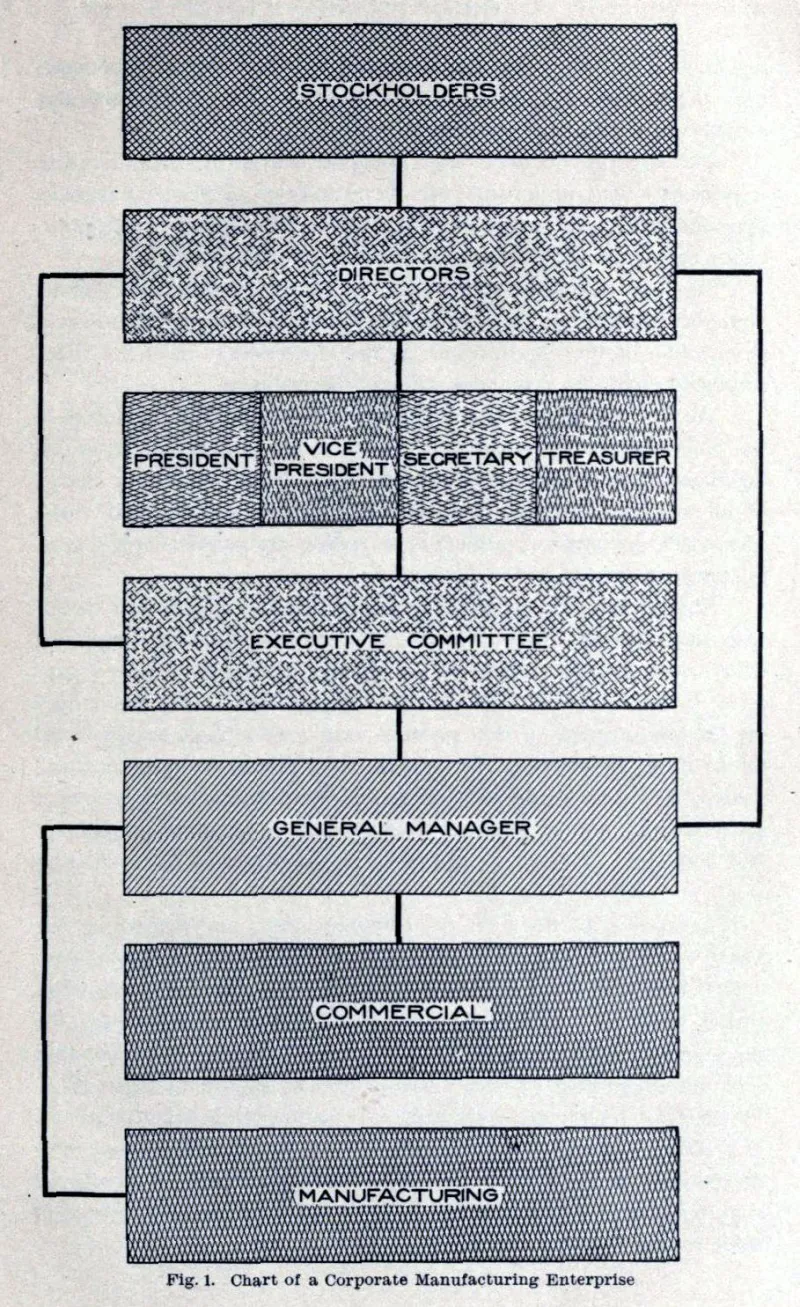
Photo: James Bray Griffith, Public domain, via Wikimedia Commons
When federal or state regulators open an inquiry, one of the first documents they request is rarely a contract or a policy manual. It is the organizational chart. The reason is simple: hierarchy, not job titles, determines where legal responsibility actually settles. A Vice President of something obscure may carry less exposure than a manager who informally approved every shipment decision for three years. Yet most companies build their org charts for payroll convenience, not for legal defensibility.
Hierarchy Is Evidence
Consider a pattern we see repeatedly: a mid-sized manufacturer faces an environmental compliance question from a state agency. The company's formal structure shows a compliance officer reporting to the COO. But in practice, plant managers routed environmental decisions through a production supervisor because he "knew the permits cold." No one updated the chart. No one documented the delegation.
When the agency arrives, it does not ask who held the compliance title. It asks who made the decisions. Email trails, approval chains, and meeting invites tell that story. The company's informal structure becomes the government's theory of the case — and the formal chart becomes evidence that the company either didn't know its own operations or deliberately obscured accountability.
This dynamic extends beyond regulators. In internal investigations, plaintiffs' discovery, and even insurance coverage disputes, the de facto reporting line is the one that counts. Courts and agencies assign weight to how authority actually flowed, not how the PowerPoint depicted it.
Where Vague Lines Create Exposure
Three structural patterns generate the most trouble:
Dotted-line ambiguity. Shared or matrixed reporting arrangements are efficient until something goes wrong. If two executives each assumed the other owned a risk — data privacy, say, or vendor oversight — the gap between them is where liability incubates. Regulators have little patience for organizations that cannot say who was responsible for a regulated function.
Shadow authority. Long-tenured employees accumulate informal power. A controller who has "always" signed off on vendor contracts may lack any documented authority to do so, yet the company is bound by the practice. When the practice is unlawful, the absence of formal authorization is not a defense; it is evidence of governance failure.
Title inflation and deflation. A manager titled "Coordinator" who negotiates seven-figure supplier terms creates a mismatch between apparent and actual authority. Counterparties, courts, and agencies will hold the company to what the person did, not what the business card said.
Auditing the Chart as a Legal Document
We recommend clients treat the org chart the way they treat their minute books: as a governance record, reviewed on a schedule and corrected deliberately. A practical audit has four steps.
First, map actual decision rights. For each regulated or high-risk function — safety, privacy, financial reporting, export controls — identify who initiates, approves, and escalates. Compare that to the formal chart. Every divergence is either a documentation fix or an unrecognized risk.
Second, paper the delegations. Where informal authority exists and should continue, document it: a delegation-of-authority policy, updated job descriptions, a signature authority matrix. Where informal authority should not exist, retire it in writing and communicate the change.
Third, test the escalation path. Ask a simple question for each risk area: if a problem surfaced tomorrow at 4:45 p.m., who would hear about it first, and who must the escalation reach within twenty-four hours? If the answer requires explaining a matrix to an outsider, the path is too complicated to work under pressure.
Fourth, version-control the chart. Keep dated copies. In any later inquiry, the ability to show what the structure was at a given time — and that changes were deliberate rather than reactive — materially strengthens the company's position.
The Board-Level Payoff
Directors should care about this more than they typically do. Oversight liability under Delaware law and the federal sentencing guidelines both turn on whether information systems and reporting structures actually delivered risk information to the right people. An org chart that misrepresents decision rights undermines the board's ability to demonstrate that it monitored anything meaningfully.
None of this requires rebuilding the company. It requires recognizing that the org chart is not furniture — it is a legal instrument that either clarifies accountability or conceals its absence. Companies that audit it annually spend their crises answering questions. Companies that don't spend their crises becoming one.